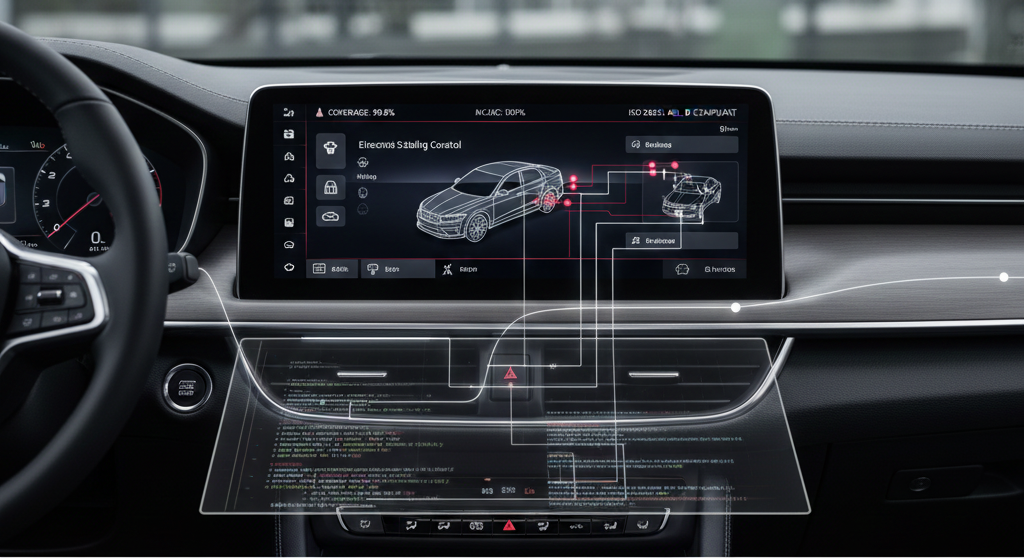
Functional Safety in Automotive: ISO 26262 Testing Best Practices
Functional safety is a non-negotiable requirement in modern automotive software development. ISO 26262 provides the regulatory framework to ensure reliability and effective risk management across vehicle electronic and electrical (E/E) systems. To meet these demands, certified tools from QA Systems, Cantata and QA-MISRA, form the backbone of robust ISO 26262 testing strategies, enabling rigorous verification, automation, and full traceability for projects targeting Automotive Safety Integrity Levels (ASIL) up to D, the highest integrity tier for critical systems such as autonomous braking and airbag deployment.
ISO 26262 Testing Principles
ISO 26262 defines a structured, lifecycle-driven verification process that begins with hazard classification and ASIL determination and continues through:
- requirements definition and bidirectional traceability
- unit and integration testing
- fault injection and robustness testing
- structural and code coverage analysis
For example, in Level 4 Autonomous Emergency Braking (AEB) systems, the lifecycle starts with item definition and Hazard Analysis and Risk Assessment (HARA), followed by measurable safety requirements mapped directly to verification activities. This disciplined approach has been critical in preventing failures such as unintended acceleration, incidents that historically led to major recalls and industry-wide safety reforms.
QA Systems: Enabling ISO 26262 Compliance
Cantata
SGS-TÜV independently certified for use up to ASIL D, Cantata automates:
- unit and integration test generation
- branch and MC/DC structural coverage
- requirements-based testing
- fault-injection and robustness validation
Cantata directly supports the confirmation review phase of ISO 26262, where independent assessors validate the effectiveness of implemented safety measures.
QA-MISRA
QA-MISRA complements Cantata by providing:
- automated static code analysis
- enforcement of MISRA C/C++ coding standards
- tool qualification kits for compliance reporting
- early detection of unsafe language constructs and resource usage
Together, Cantata and QA-MISRA deliver a certified workflow that supports ISO 26262 requirements across all ASIL levels.
Real-World Testing Examples
- Emergency Braking Systems (AEB): Automotive OEMs use Cantata to simulate sensor faults, actuator failures, and unexpected vehicle maneuvers, verifying that embedded software consistently responds within defined safety limits. QA-MISRA ensures the underlying ADAS codebase complies with MISRA rules to prevent undefined behavior before deployment.
- Electronic Throttle Control: In one documented case, ISO 26262 verification activities uncovered shortcomings in functional safety implementation, prompting revised software architectures and significantly strengthened validation processes.
ISO 26262 Testing Best Practice
To build a defensible functional safety case, automotive organisations should:
- establish bidirectional traceability between requirements, tests, and results
- adopt automation for regression, fault injection, and interface testing
- maintain comprehensive documentation using certified tools (Cantata and QA-MISRA) to streamline independent confirmation reviews
- integrate simulation methodologies (MIL, SIL, HIL) to validate fault behaviour and edge cases
- continuously update safety plans and audits to reflect new risks, technologies, and regulatory updates
By combining these best practices with QA Systems’ proven toolsets, automotive teams can confidently meet ISO 26262 requirements, safeguard public trust, and protect road users against the evolving risks of embedded vehicle systems.
Mapping QA Systems Tools to Unit, Integration, and System Testing
QA Systems tools align precisely with the classic software testing pyramid: unit, integration, and system testing.
Unit Testing
Cantata is purpose-built for automated unit testing of embedded C and C++ software. It enables verification of individual functions or modules in isolation using:
- white-box testing techniques
- branch and MC/DC code coverage
- full requirements traceability
Key capabilities include automatic test case generation, stubbing, and mocking, ensuring dependencies are controlled and each test focuses strictly on the logic under test, fully aligned with ISO 26262 expectations.
Integration Testing
Cantata extends seamlessly into integration testing by allowing multiple modules, subsystems, and APIs to be verified together. It supports:
- call interception and wrapping
- controlled fault injection
- interaction and interface validation
This ensures that not only do individual components behave correctly in isolation, but that data flows, error handling, and interfaces remain robust, as required for ISO 26262 item integration.
System Testing
While Cantata focuses primarily on unit and integration levels, its outputs form the foundation of system-level qualification evidence. For full system validation:
- Cantata provides low-level dynamic test and coverage evidence
- QA-MISRA supplies coding-standard compliance evidence
- Both tools contribute traceable, auditable artefacts required for final system certification
Together, they ensure that system-level safety is built on verified, standards-compliant software from the earliest phases of development.
Summary Table
| Test Level | Main QA-Systems Tool | Capability Highlight |
| Unit Testing | Cantata | Isolate modules, auto-generate tests, and coverage analysis |
| Integration Testing | Cantata | Combine modules, wrap/call intercept, interface testing |
| System Testing | Cantata & QA-MISRA | Evidence & compliance for system qualification |
Together, Cantata and QA-MISRA provide end-to-end ISO 26262 verification, from precise code-level correctness to system-level safety assurance with certification-ready evidence.
© 2025 QA Systems. Published by JORAL Technologies.
RELATED NEWS
Setting Up a QA-MISRA Evaluation License and VS Code Extension
The following steps explain how to activate a QA-MISRA evaluation license, configure the local server, install the QA-MISRA extension in Visual Studio Code, and run an example analysis. 1. Requ[...]
Read more
Using QA-MISRA to Bring Coding Standards into C/C++ Development
In embedded and safety-critical software, coding standards help reduce risky language behaviour, improve consistency, and make software easier to review and verify. This is especially important i[...]
Read more
When Breakpoints Aren’t Enough: Debugging Faster with ULINKpro Trace
Most embedded developers are familiar with the usual debugging cycle: set a breakpoint, stop the processor, inspect the problem, make a change, and try again. That works well until the problem [...]
Read more
How Static Analysis Supports DO-178C Verification
Developing software for airborne systems requires strong verification evidence, especially for higher-criticality applications. DO-178C defines objectives for airborne software development and ve[...]
Read more
Installing and Using AbsInt Astrée with Visual Studio Code
AbsInt Astrée can be integrated with Visual Studio Code using the A3C extension, allowing developers to run Astrée analysis and review detected alarms directly within the editor. Install and Con[...]
Read more
EMBEDDED IS EVERYWHERE
PRODUCTS
Manufacturers
Resource center